Establish and Document How the Application Handles Regulated Data Such as PII, PHI, PCI, and PFI - Application Management Best Practices
Establish and Document How the Application Handles Regulated Data Such as PII, PHI, PCI, and PFI
(Chapter 125 of Application Management Best Practices)
Executive Summary: Chapter Overview
IF4ITThe Bottom Line
Core Concepts
| Concept | Definition & Strategic Role |
|---|---|
| Regulated Data | Data whose handling is governed by laws, regulations, and industry standards, with PII, PHI, PCI data, and PFI as common examples. Risk and Compliance determines which forms apply, since an Application may hold others. |
| Regulated Data Controls | The controls meeting the obligations for each form of regulated data, such as encryption, masking, access restrictions, and audit logging, recorded with how each is implemented and verified in the Security and data sections of the Application Documentation. |
| Data Minimization | Ensuring the Application holds only the regulated data it needs. Together with defined retention and purging consistent with the Application’s retention rules, it limits exposure and the scope of obligations. |
| Non-Production Data Protection | Preventing non-production Instances from exposing real regulated data, for example through masking or synthetic data. Instance differences are recorded explicitly so regulated data does not leak into test environments. |
Quick Q&A
Question: What must be established for each form of regulated data an Application holds, processes, or transmits?
Question: Where is an Application's regulated data classification recorded, and when is its handling reviewed?
Read More Below
This chapter explains how to establish and document how an Application handles regulated data.
Many Forms of Regulated Data
There are many forms of regulated data, defined by laws, regulations, and industry standards across industries and jurisdictions. The most common examples are:
Personally Identifiable Information (PII): information that can identify an individual.
Protected Health Information (PHI): health information about identifiable individuals.
Payment Card Industry (PCI) data: payment card and cardholder data.
Personal Financial Information (PFI): financial information about identifiable individuals.
These are examples only; an Application may hold other forms of regulated data, and the enterprise’s Risk and Compliance function should determine which forms apply.
Establish How the Application Handles Regulated Data
For each form of regulated data the Application holds, processes, or transmits, establish, with Risk and Compliance and Security:
Where the data is stored, processed, and transmitted, including across Integrations and in non-production Instances.
The obligations that apply, and the controls that meet them, such as encryption, masking, access restrictions, and audit logging.
How the data is minimized, so that the Application holds only what it needs.
How long it is retained, and how it is purged, consistent with the Application’s retention rules.
How individuals’ rights, such as access or deletion requests, are honored where they apply.
How breaches are detected, reported, and handled.
How non-production Instances avoid exposing real regulated data, for example through masking or synthetic data.
Document and Share Regulated Data Handling
Record the regulated data the Application handles, the obligations and controls that apply, and how each is implemented and verified, in the Security and data sections of the Application Documentation, with Instance differences recorded explicitly. Record the regulated data classification in the Application Record. Review regulated data handling with every Release and whenever obligations change.
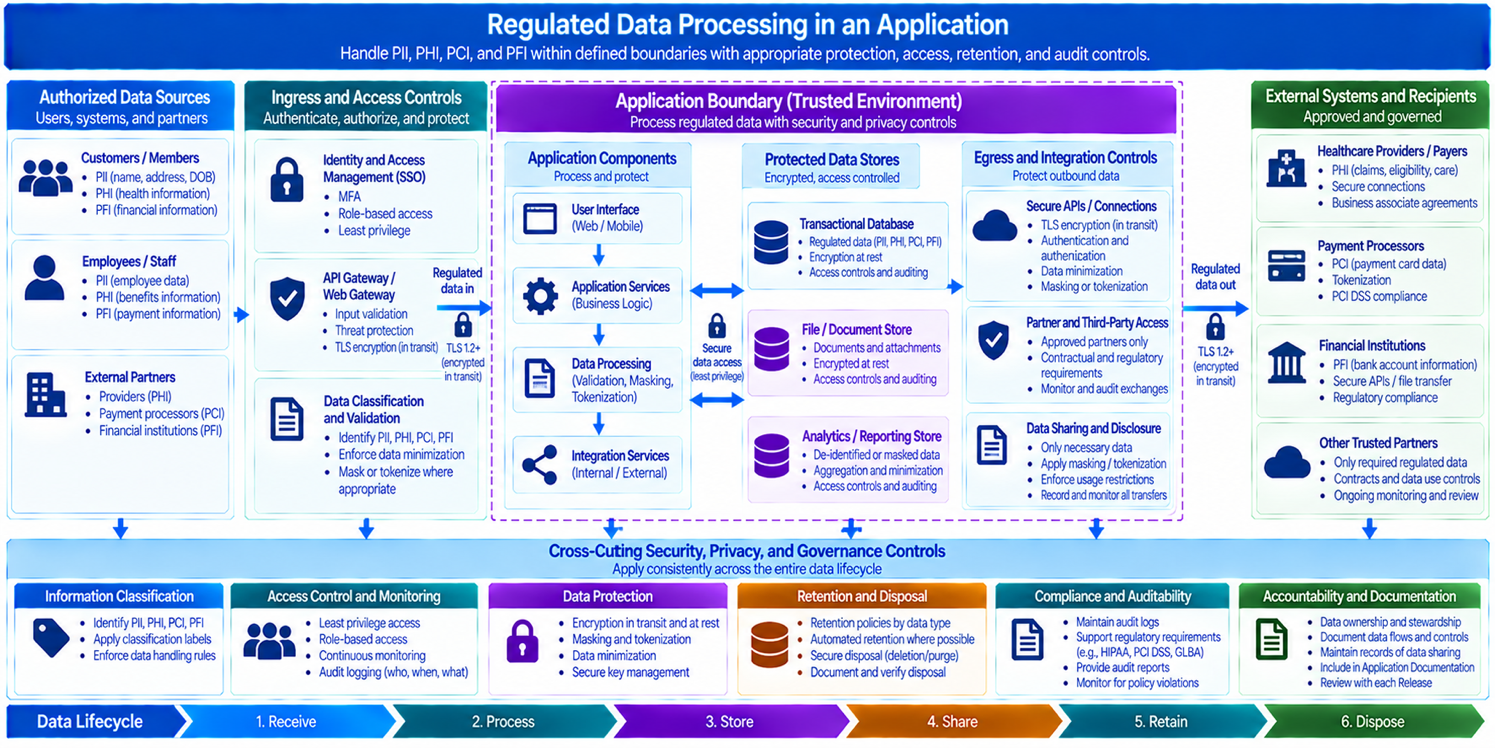
Best Practice: Establish and Document How the Application Handles Regulated Data
It is a best practice to both establish and document the solution for an Application’s regulated data: identify every form of regulated data it handles, and record where that data lives and flows, the obligations and controls that apply, how it is minimized, retained, and purged, how individuals’ rights and breaches are handled, and how non-production environments are protected.
Benefits: Documented regulated data handling lets the enterprise demonstrate compliance, respond to individuals’ requests and breaches quickly and correctly, and avoid the penalties and reputational damage that follow mishandled data. Knowing where regulated data flows also prevents it from leaking into places, such as test environments and logs, where it is not protected.
Connections to Related IF4IT Practices and Inventories
The Data and Information Inventory and Attributes describes how data and information types, including their sensitivity, are recorded. The Regulatory Agencies Inventory and Attributes describes the regulatory bodies whose rules may apply.
How to cite this page
When referencing this page in academic work, internal standards, or external publications, include the page title, IF4IT as author and publisher (The International Foundation for Information Technology (IF4IT), LLC), the URL, and your access date.
Example (informal web citation):
The International Foundation for Information Technology (IF4IT), LLC. Establish and Document How the Application Handles Regulated Data Such as PII, PHI, PCI, and PFI | Application Management Best Practices. https://if4it.org/best-practices/application-management-best-practices/establish-and-document-how-the-application-handles-regulated-data-such-as-pii-phi-pci-and-pfi/ (accessed 2026-10-31).
See About Us for content governance and site-wide citation guidance.
Copyright for The International Foundation for Information Technology (IF4IT), LLC: 2008 - Present
Legal Disclaimers